

Don’t wanna read the entire article? Prefer video? Check out the video below.
Honest question: when was the last time you actually opened your WISP? Not renamed it. Not moved it into a new folder. Opened it, read it, and changed something.
If your answer includes the words “when I first wrote it,” you are in very good company. For a lot of practices, the Written Information Security Plan lives the same life as a January gym membership (paid for, sincerely intended, quietly untouched).
Fall is the best time of year to fix that. Once October 15 is in the rearview mirror, there is a short, calm window before filing season, and the news cycle has handed us a stack of fresh reasons to care. Let’s dig into why now, what the latest breaches teach a small practice, and how to give your plan a real checkup before January.
Why This Fall, Specifically
Three things line up right now, and together they make the case better than I could.
1. PTIN renewal is coming, and it asks you about your plan
Every 2026 PTIN expires December 31. Renewal season for 2027 should open in the next few weeks (last year it opened at the end of October). When you renew, line 11 of Form W-12 asks you to check Yes or No: are you aware that paid preparers are required by law to create and maintain a written information security plan? The form points you to Publications 5708 and 4557, and the whole application is signed under penalties of perjury. If you are renewing online which most of us are, you receive the same question.
Translation: the IRS is not asking whether your plan is perfect. It is making sure nobody can later say they didn’t know. That checkbox is a lot more comfortable to click when the plan it refers to reflects the practice you actually run today.
2. The IRS just finished its annual reminder tour
The Security Summit ran its five-week “Protect Your Clients; Protect Yourself” series this summer, now in its 11th year. Week three was devoted entirely to WISPs. In IR-2026-92 (Aug. 18, 2026), the IRS repeated that federal law requires tax and accounting professionals to create and maintain a WISP. It also said firms should review, test, and update the plan regularly, adjusting it for changes in operations or the results of security testing.
A WISP is not a document you write once. It is a document you keep writing.
3. Filing season is when you’ll have the least time and the most risk
The series wrapped up with IR-2026-111 on Sept. 16. It lists the schemes still landing in practitioner inboxes: fake “new client” emails carrying malicious attachments, phishing aimed at your EFIN, PTIN, and CAF number, and IRS impersonation by email, text, and phone. Those peak when inboxes are fullest and patience is thinnest. Update the plan in October, and your team trains on it before the flood instead of during it.
The News Is Doing the Teaching for Us
Two stories from the last few months deserve a closer look. Not because your practice looks like the Pentagon or a Big Four firm, but because the failures behind them are painfully ordinary.
The Pentagon’s unencrypted file share
The Department of Defense confirmed a breach of a Defense Manpower Data Center system affecting 2.76 million living people and roughly 294,000 deceased people (Cyber Security News). Unauthorized users got in through a vulnerability in a file-sharing system and had access from October 2025 until the flaw was found on July 16, 2026. The files held unencrypted names, Social Security numbers, and dates of birth. Notice letters were dated September 18.
Let’s dig into what that means for a practice our size:
Roughly nine months of access before anyone noticed. If someone had been quietly reading your client folders since last October, what in your setup would have told you?
The data was not encrypted at rest. That is the difference between “someone reached a server” and “someone walked off with Social Security numbers.”
The entry point was a file share. Not an exotic, movie-plot attack. A place documents were kept because it was convenient.
(If the Department of Defense can leave a folder unencrypted, the rest of us can stop feeling quite so embarrassed about our own to-do lists. Then we should go do them.)
EY’s help desk turned into a filing cabinet
In July, Ernst & Young began notifying clients that an unauthorized party had gotten into a third-party IT support ticket platform used by its IT staff (BleepingComputer). The intruder downloaded documents between March 28 and April 12, 2026. EY spotted the anomalous activity on April 23. The files contained personal and financial data in, or used to prepare, client tax filings.
Why was tax data sitting in a help desk system at all? Because support tickets carried attachments, and nobody’s plan said they shouldn’t.
Translation for the rest of us: your data lives wherever your people put it, not wherever your WISP says it lives. That includes the screenshot you sent your IT person, the client PDF attached to a software support case, and the return you uploaded to a vendor’s portal to troubleshoot a rejection.
Your WISP describes where client data is supposed to be. A breach finds out where it actually is.
Why I Don’t Lead With the Fines
I love teaching this topic, mostly because of what happens afterward. My inbox fills up with questions from tax pros who genuinely want to get it right. Nobody writes to say they’re terrified. They write to say, “I want to do the right thing, and I’m not sure where to start.”
That tells me something important. People want to protect their clients. They don’t need to be scared into it.
So I don’t open with penalties. Yes, the FTC can fine you. But let’s dig into where the FTC actually spends its time:
The FTC says it has brought more than 90 data security enforcement actions to date, across every industry it oversees (FTC, Feb. 2026). Recent examples it highlights include GoDaddy and an education technology company.
Compare that with the more than 800,000 paid tax preparers who renew a PTIN every year (Ohio Society of CPAs).
The FTC’s best-known tax prep case, TaxSlayer in 2017, involved an online tax platform where hackers took over nearly 9,000 customer accounts.
Translation: the FTC generally goes after large platforms with large numbers of affected consumers. That could shift (FTC Chairman Andrew Ferguson told MLex in June that he expects a surge of privacy cases in the second half of 2026), but the odds that a three-person office is next on the list are small.
What actually happens to small practices
The consequences that reach small firms tend to come from somewhere else: clients, plaintiffs’ lawyers, and your own reputation.
This spring, a small tax and accounting firm in Washington state reported that data for 18 clients had been stolen and used to file fraudulent returns. By September, a class action law firm was publicly inviting affected clients to come forward (Claim Depot). Eighteen clients.
In February, a New Jersey accounting firm was hit with a proposed class action alleging it failed to safeguard client information and was slow to send breach notices (Law360).
Plaintiffs’ firms now open “investigations” whenever a small accounting practice turns up in a state breach filing or on a ransomware leak site. September alone brought several (ClassAction.org).
The deeper cost is trust. Clients forgive a lot. It is much harder to forgive a phone call that starts with “someone filed a return in my name, and they got my information from your office.”
The FTC may never learn your name. Your clients, their families, and everyone they would have referred to you will.
That’s why I teach this from the client’s side of the desk. A WISP isn’t paperwork you do for Washington. It’s how you keep a promise to people who trusted you with everything.
What Changed Since You Wrote It?
Most WISPs I look at aren’t wrong. They just describe a practice that no longer exists. Here is what has probably changed in your office since the plan was last touched:
AI tools. If anyone on your team pastes client facts into a chatbot, uses an AI notetaker on client calls, or runs returns through an AI review tool, those are new places client data flows. Your plan should name them, say what is allowed, and address the §7216 questions before a client asks you about them.
New vendors. A new client portal, e-signature service, practice management platform, or outsourced bookkeeper. The FTC expects you to choose service providers that can protect the data and to require that in their contracts (IR-2026-92).
New devices. Laptops, phones, tablets, and yes, the smart TV in the conference room. (I wrote a whole piece on that last one: “Your Television Is a Computer. You Just Never Treated It Like One.”)
New people and new places. Seasonal staff, a remote hire, a temporary home office that quietly became permanent. Each one changes who has access and from where.
Authentication. The IRS spent a full week of the summer series on multifactor authentication and IP PINs (IR-2026-106). If a system touching client data offers MFA and you haven’t turned it on, that belongs in this year’s update.
If any of those made you wince a little, good. That wince is your risk assessment getting started.
Your One-Hour WISP Checkup
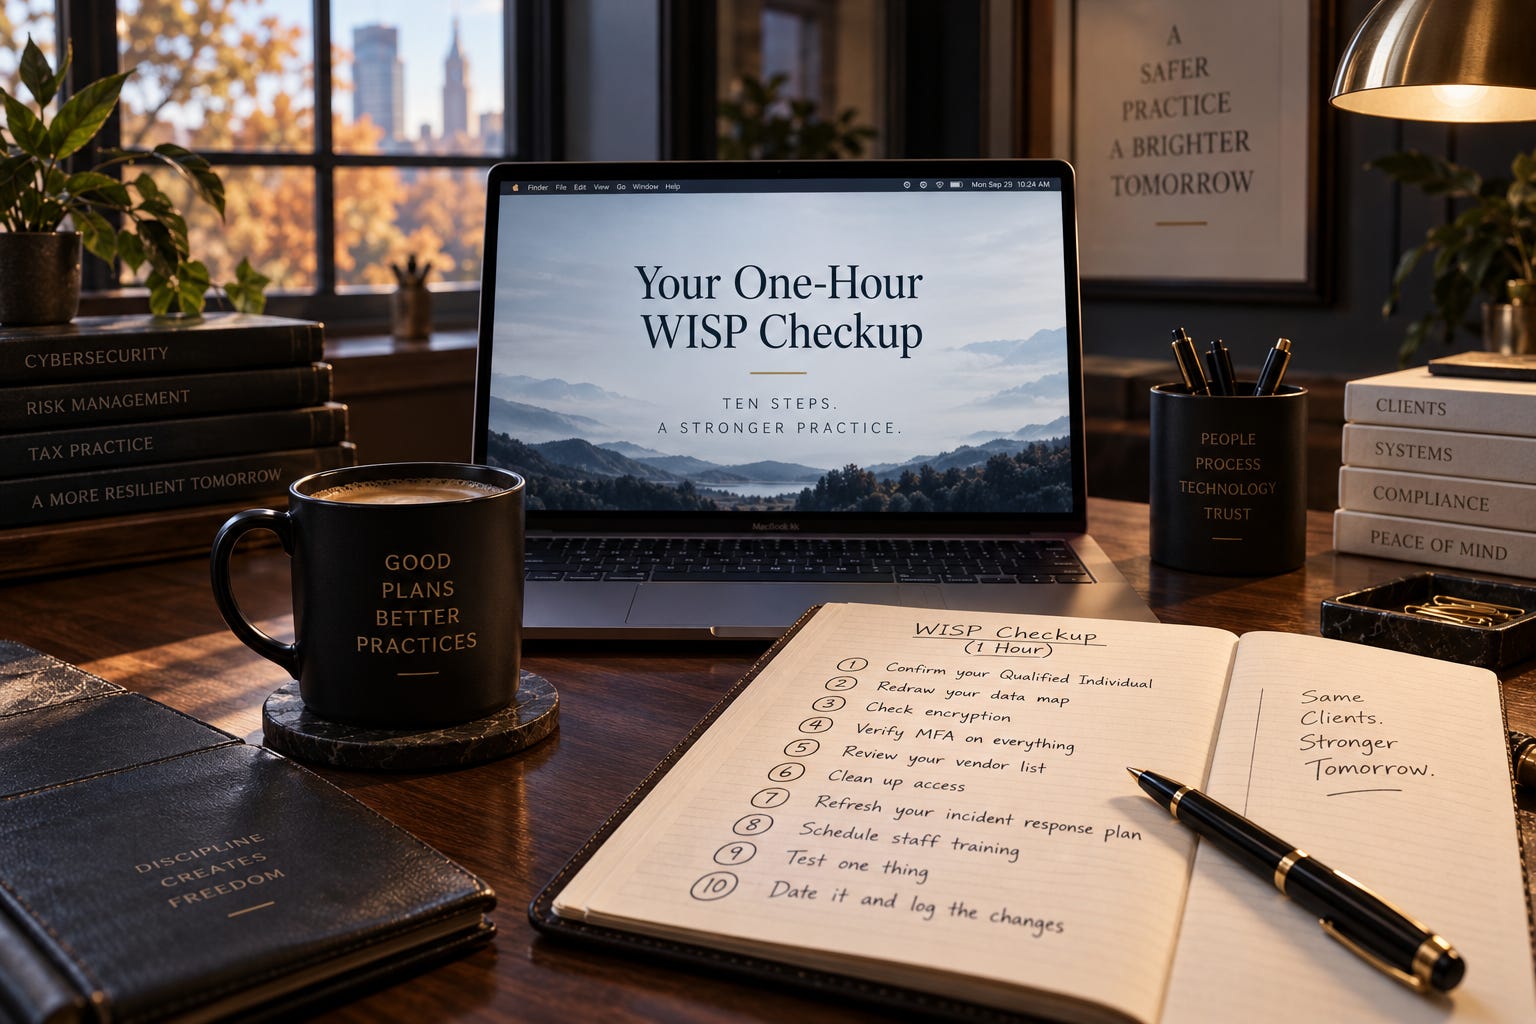
You don’t need a weekend for this. Block one hour, get a coffee, and walk through these ten steps with your current plan open beside you.
Confirm your Qualified Individual. The Safeguards Rule requires a designated person to coordinate the program. Is it still the right person, and do they know it’s them? (Solo practitioners: congratulations, it’s you.)
Redraw your data map. List every place client data lives or passes through: tax software, document storage, email, portal, e-signature, backups, AI tools, and the support tickets you send vendors. Compare that list to what your plan says.
Check encryption. Laptops, external drives, backups, and file shares, both at rest and in transit. The Pentagon lesson applies at every size.
Verify MFA on everything that touches client data. Tax software, email, cloud storage, remote access, and your IRS online accounts.
Review your vendor list. For each service provider, confirm how they protect data and that your agreement requires it.
Clean up access. Remove former and seasonal staff. Make sure current staff can reach only what their role needs.
Refresh your incident response plan. Add your IRS Stakeholder Liaison, the Federation of Tax Administrators’ Report a Data Breach page, and your state’s notice rules. Note the FTC requirement to report a security event affecting 500 or more people, generally within 30 days of discovery.
Schedule staff training before January. Use the warning signs in IR-2026-111 as your syllabus: fake new clients, EFIN, PTIN, and CAF phishing, and IRS impersonation.
Test one thing. Restore a file from backup, or run a quick phishing drill. A plan you’ve never tested is a plan you are hoping works.
Date it and log the changes. Record what changed and why. Future you (and any insurer, examiner, or eventual buyer of your practice) will want that history.
If you are starting from scratch, Publication 5708 is the IRS template built for smaller practices. And if your firm maintains information on fewer than 5,000 consumers, the Safeguards Rule (16 CFR 314.6) excuses you from a few formal items, including the written incident response plan. The IRS still recommends a data theft response plan anyway, and so do I.
The goal isn’t a perfect document. It’s an honest one that matches the practice you run today.
Something I’ve Been Building
A small confession. Every time I teach this topic, the same thing happens. People leave motivated, open a blank template, and stall somewhere around page two.
So I’ve been building a WISP builder made for real tax practices.
It isn’t ready to share yet, but it’s close. It is currently in testing and will launch in November. Subscribers will be the first to hear about it. In the meantime, if there is a part of your WISP that has always stumped you, reply and tell me. I’m building for exactly those moments.
Where You Can Find Me
Tue., Oct. 6, 2026, 10:00 a.m. to 12:00 p.m. PT
Brass Tax Ethics webinar, “Ethics in the Real World.” Circular 230, due diligence, and the decisions that get preparers in trouble. 2 hours of CE/CPE (CPA, EA, and CRTP eligible), no assessment test required for the live session, $89.
Wed., Oct. 14, 2026, 2:30 to 4:40 p.m. ET
myLawCLE: The IRS’s First AI Rules: Circular 230 Exposure After OPR Alert 2026-19.I’m excited to be co-presenting with Sharyn M. Fisk, former director of the IRS Office of Professional Responsibility. We’ll cover how AI-assisted tax work falls under existing Circular 230 authority, and the documentation, billing, and supervision safeguards firms can apply now.
Oct. 25 to 27, 2026: NYSSEA 39th Annual Conference. Gideon Putnam Resort, Saratoga Springs, NY. I will present a class on penalty abatement and co-present with Matt Metras, EA, USTCP, on Tax Practice Automation & Tech Hacks to Save Your Sanity.
Tue., Nov. 10, 2026, 9:00 a.m. to 12:30 p.m. CT
NATP webinar workshop, Real-World Digital Asset Reporting. 4 CPE. Form 1099-DA, reconciliation, and basis documentation.Dec. 1 to 3, 2026: NATP TaxCon. NATP’s online conference on AI, IRS technology, and responsible technology use in tax practice. I’m on the “Voices from the Profession” panel (Dec. 1), presenting on Section 7216 and protecting taxpayer information in technology-assisted workflows (Dec. 2), and joining a panel on building service lines beyond the tax return (Dec. 2). More details to come.
More classes and a few open slots
I’m looking forward to teaching more on this subject in the months ahead and will post updates to my schedule.
And because so many of you email me after these classes, I’ve opened my booking system for a few slots for tax pros who want to talk through their WISP or other questions one-on-one. They’re limited, so if you’ve been sitting on a question, this is the time to ask it. You can book here.
The Plan You Actually Follow
Here is what I keep coming back to. Neither breach above started with a brilliant hacker. Each started with an ordinary shortcut nobody revisited: a file left unencrypted because it was convenient, an attachment dropped into a ticket because it was quicker. A WISP exists to catch those shortcuts before they turn into headlines, and it can only do that if it describes the practice you actually run.
So before you check that box on your PTIN renewal this fall, give yourself the hour. Open the plan. Fix one thing that is no longer true. Then put next year’s review on the calendar. Our clients hand us their most sensitive information, and keeping this document honest is one of the quietest ways we keep faith with that trust.